From the blog
Notes, experiments and behind-the-scenes from the studio.
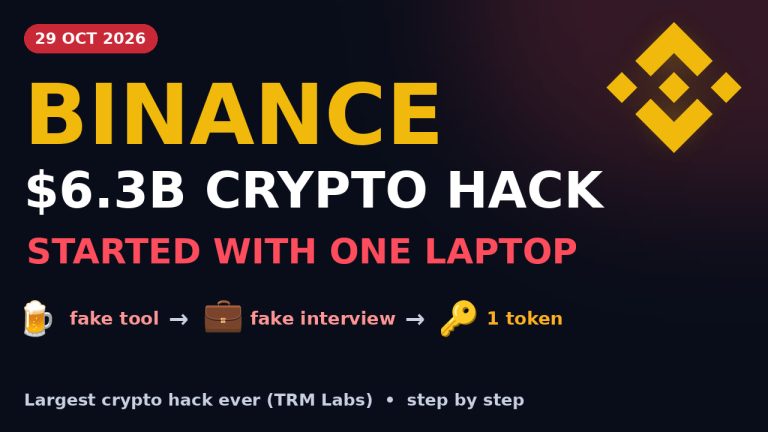
The $6.3B Binance Hack Started With One Laptop: Fake AI Tool, Fake Job Interview and One Token
According to Binance's initial findings, the largest crypto hack on record began five months earlier with a developer searching for an AI coding tool. The attack path step by step, and five lessons for every developer.
Read more →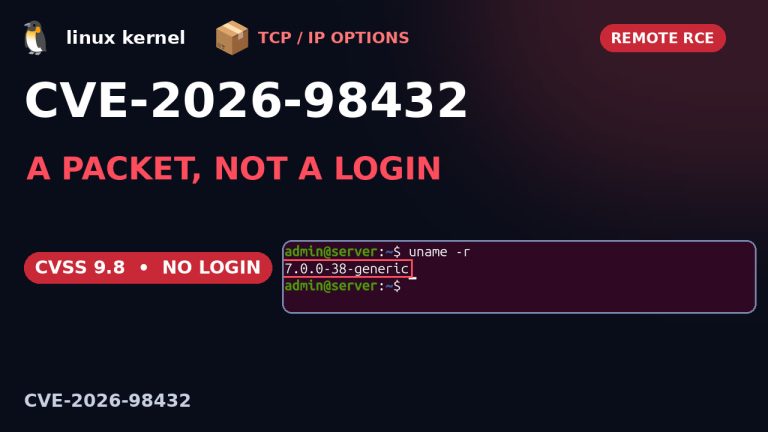
CVE-2026-98432: A Single Packet, No Login: The 9.8 Linux Kernel TCP Bug and How to Protect Your Server
A use-after-free in the Linux kernel's TCP connection setup can be reached by a crafted packet before any login. What it is, why Ubuntu's fix isn't out yet, and the stopgaps you can apply today.
Read more →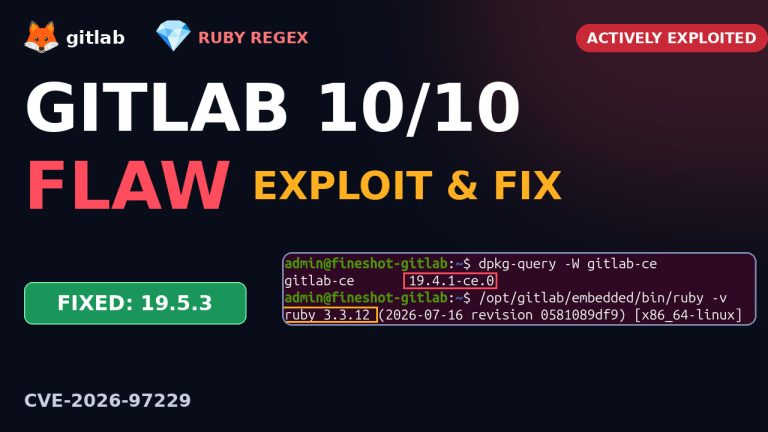
The GitLab 10/10 Flaw (CVE-2026-97229, GitLab2Shell): Why Updating GitLab Might Not Be Enough
One crafted regular expression in a CI/CD config can run code on a self-hosted GitLab server, no login needed. Alpine Linux updated and was still vulnerable. How to check, upgrade and verify.
Read more →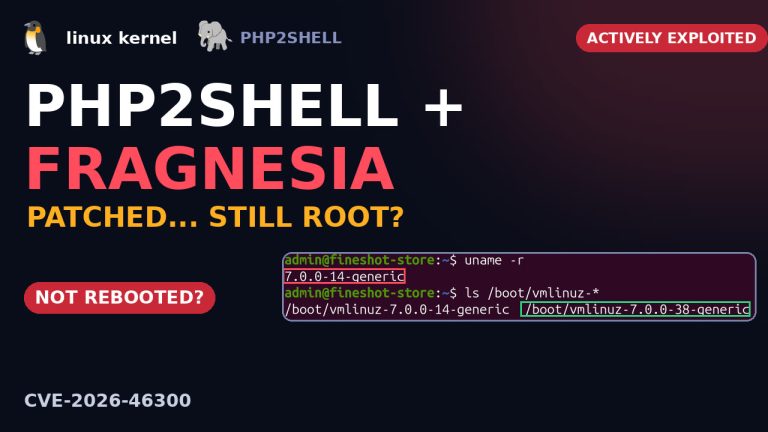
PHP2Shell + Fragnesia: Patched Linux Servers That Are Still Vulnerable to Root (CVE-2026-46300)
Attackers chain PHP2Shell (into your website) with Fragnesia (a Linux kernel bug) to get root. The kernel fix came out in May, yet servers still get hit, because the fix is installed but never running.
Read more →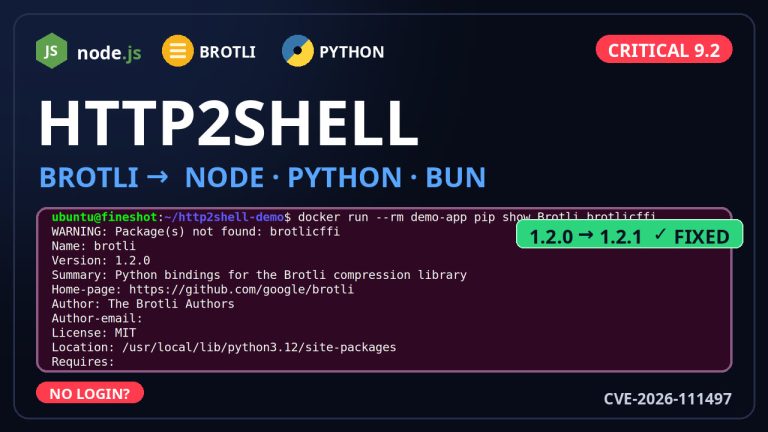
HTTP2Shell: How the Node.js Brotli Bug Spread to Python, Bun, Envoy and More
Node2Shell grew into HTTP2Shell: the same Brotli decoder bug (CVE-2026-111497) reaches Python HTTP clients, Bun, Envoy, Istio and curl. Who is exposed, how to check in one minute, and the fixed versions.
Read more →
The eMudhra Certificate Incident Explained: Weak Keys, a Distrusted Root, and What It Means for Your Site
Eight eMudhra intermediate CA keys were so weak they could be cracked in under a second. Browsers distrusted the emSign ECC Root CA G3, and eMudhra is exiting the global SSL/TLS business. What happened and what to check.
Read more →